Posts

%PLATFORM_UCAST-4-PREFIX: --------- TCAM 3750 Switch

Image
 %PLATFORM_UCAST-4-PREFIX:  One or more, more specific prefixes could not be programmed into TCAM and are being covered by a less specific prefix, and the packets may be software forwarded So what is TCAM ? Ternary Content Addressable Memory is used in multi-layer switching also know as Layer 3 switching. The switches forward the packets and frames at the speed of the line by using ASIC hardware. Normally switches make there forwarding decisions based on Layer 2. TCAM is used for Layer 3 components and other features such as QOS and ACES ( Access List ).  Check TCAM and usage of templates being used in the device.  show sdm prefer ? ! This will show us the templates that can be used in the device to give more resources to one feature or the other. For example the default is the equal resource distribution while the routing gives more resources to Layer 3 routing. show sdm prefer ! The command without the "?" will show us what we are cu...
Configuration Fractional T1 PRI

Below is a configuration for a T1 PRI that has both voice and data running across the circuit. This was tested in a lab environment. ! Global configuration isdn switch-type primary-ni ! This is the primary configuration for switch type for United States card type t1 0 0  ! This configuration sets the card type of the installed called. "0' and "0"  OR "zero" and "zero" represent the card information of the slot and sub slot. You can get this information by doing a show inventory or show diag. show inv NAME: "CISCO2901/K9 chassis", DESCR: "CISCO2901/K9 chassis" PID: CISCO2901/K9      , VID: V06 , SN: NAME: "VWIC3-2MFT-T1/E1 - 2-Port RJ-48 Multiflex Trunk - T1/E1 on Slot 0 SubSlot 0 ", DESCR: "VWIC3-2MFT-T1/E1 - 2-Port RJ-48 Multiflex Trunk - T1/E1" PID: VWIC3-2MFT-T1/E1  , VID: V01 , SN:  controller T1 0/0/1 cablelength short 110 channel-group 11 timeslots 11-20 ! ...

UCCX and CUCM 9.0 Integration Steps ( Pre check)

Login to CUCM Serviceability Go to Service Activation Turn on AXL Web Service Go to CUCM Unified CM Admin Page : Create ACG  Create an Access Control Group Usesr Management > User Settings > Access Control Group Assign roles to the group using the "Related Links" drop down in the upper right hand corner Assign Standard AXL API Access Create an Application User User Management > Application User Create user for AXL Access  Assign Role to user for Access Control Group made Create user for AXL Access Save user Create End User Create End User that will be used for the admin account Have license file ready  Once done begin the steps for the setup wizard on the CCX administration page 

Quick IP Address Subnetting a /24

Had a client that needed a range of IP's specifically 8.  The only trouble was getting a block that would suffice out of the /24 and distribute it into chunks. If you're handy with math and understand CIDR / Subnetting this is an easy way to get your numbers quickly. Lets say our range is 1.1.1.0/24  and we need a total of 8 ip's ( 6 usable ). What is the subnet mask going to be? Well there are 256 TOTAL numbers of bits on or off in an octect (X.X.X.X each x represents an octet) to make up an actual number. 0 through 255   = 256 total because we count 0 So simple math: I need 8 right ? 256 -  8 = 248 Subnet mask = 255.255.255. 248 Now we just need to find a block or range.  Lets say we want to have 200 as a range. If you just take that number (200 for example) and divide by 8 you will see if it goes into it evenly or not. If it does this is the starting network address. For example = 200 /  8= 25 EVENLY     ...

IPS Module Sync NTP Server Error

Image
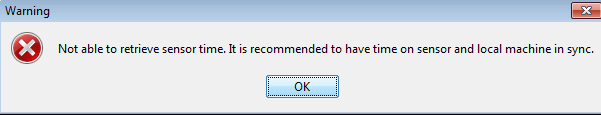
So working on an IPS module. I finally got it up and running with a reload and install of an upgrade package. However the NTP server would not sync even though it was configured correctly! When adding an IPS module to the IPS Manager Express you may come across the following error.  In order to fix this we need to re-associate the time clock and make sure that the local host and the IPS are actually in sync. What to check: 1. Check NTP Configuration  IPS# sh clock - Check clock to make sure it is in sync or not with the actual NTP Server / ASA host 14:44:29 GMT-06:00 Tue May 28 2013 IPS# sh statistics host - Check the configuration of the host to make sure that it is actually synchronized and associating to the correct NTP source General Statistics    Last Change To Host Config (UTC) = 28-May-2013 18:18:06    Command Control Port Device = Management0/0 Network Statistics     = ma0_0     Link encap:Ethernet ...

Basic Step of SIP Trunk / H323 Gateway

Below is the IOS configuration from my lab for a SIP trunk to the sip provider and h323 gateway configured in Call Manager: **** This is only for incoming calls. Outbound call isn't fully configured. Voicegateway Configuration: ! ! ! ip domain name lab.local ip name-server 8.8.8.8 ! ! voice call send-alert voice rtp send-recv ! voice service voip   allow-connections h323 to h323  allow-connections h323 to sip  allow-connections sip to h323  allow-connections sip to sip  h323  sip   bind control source-interface FastEthernet0/0   bind media source-interface FastEthernet0/0 ! ! ! ! voice class h323 1 ! ! ! ! ! voice translation-rule 1  rule 1 / Inbound PSTN Number / /4200/ ! ! voice translation-profile CALLED  translate called 1 ! ! ! ! ! ! archive  log config   hidekeys ! ! ! ! ! ! interface FastEthernet0/0  description Main Link to Switch  ip address ...

Wireless Radius Authentication - Client can't connect to wireless network.

Image
So the masses are just screaming. They can't connect to the wireless SSID. Gather the client's MAC from their wireless network connection: CMD: (In windows command prompt)  - ip config - scroll to wireless connection To begin its time to debug! CMD : debug client <MAC ID> Example : debug client 11:22:33:44:55:66  After a debug we can see the clients' authentication or errors based on the MAC addressed defined. Below is a debug of the client having issues: Authentication has exceeded its maximum attempts. This leads me to check into the radius server before changing any settings for attempts or timing values ( which can be a problem as well ).  Low and behold the radius server had an expired authentication certificate.